CAN-SPAM penalties run up to $53,088 for each email that breaks the law, the FTC’s maximum civil penalty in 16 CFR 1.98 (current eCFR text, read on 3 November 2026). That is a maximum, not a price: in August 2024 the FTC called its $2.95 million penalty against Verkada the largest it had obtained for a CAN-SPAM violation. States can also claim up to $250 per unlawful email to their residents, affected internet access services up to $25 or $100, and some practices are crimes.
In my view, the mistake is pricing your risk off one number: multiplying $53,088 by your list, or deciding nobody gets fined for cold email. The FTC’s compliance guide says “The law makes no exception for business-to-business email.”
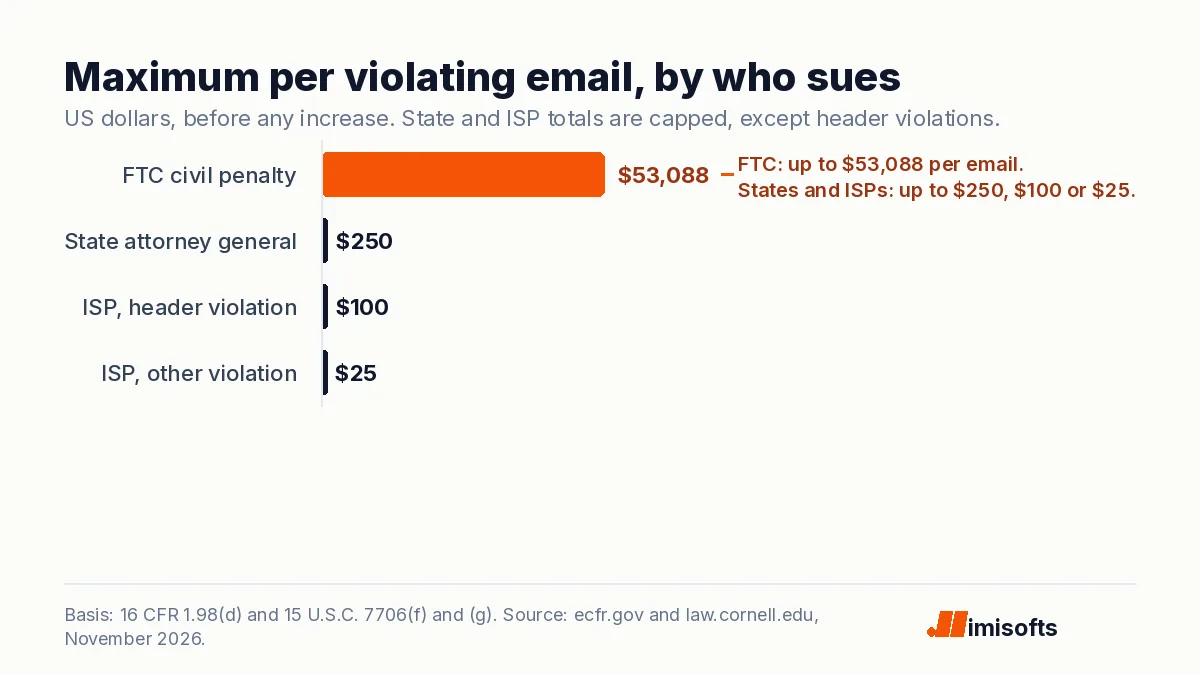
$53,088 is the FTC’s per-email maximum, not a rate. State and internet access service amounts are maximums too, and most are capped.
Key numbers
| Item | Number |
|---|---|
| FTC civil penalty, per violating email (maximum, for penalties assessed after 17 January 2025) | $53,088 |
| Largest FTC CAN-SPAM penalty, per the FTC in August 2024 (Verkada) | $2.95 million |
| Verkada penalty per email sent (more than 30 million commercial emails over three years, as alleged, per the FTC) | Under 10 cents |
| Experian Consumer Services settlement, August 2023 (settled FTC charges: email with no way to opt out) | $650,000 |
| State attorney general, per unlawful email to residents (or actual loss, if greater) | Up to $250 |
| State attorney general cap on the per-email amount (not for header violations; a court may raise it up to three times) | $2,000,000 |
| Internet access service, header violations (no cap) | Up to $100 per email |
| Internet access service, other violations (capped at $1,000,000; a court may raise it up to three times) | Up to $25 per email |
| California recipient, unsolicited email ad (B&P 17529.5) (sent from or to California; third-party domain, false headers or a knowingly misleading subject line; up to $1,000,000 per incident) | $1,000 per email |
| Maximum prison term, 18 U.S.C. 1037 (if the offense furthered a felony or followed a prior conviction) | Up to 5 years |
| Deadline to honor an opt-out (per the FTC compliance guide and 15 U.S.C. 7704(a)(4)) | 10 business days |
| Opt-out mechanism must keep working (after you send the message) | At least 30 days |
Read on 3 November 2026 from 16 CFR 1.98 on eCFR, 15 U.S.C. 45, 7704, 7706, 7707 and 18 U.S.C. 1037 on LII, California Business and Professions Code 17529.5, the FTC compliance guide, the FTC releases on Verkada and Experian and the Justice Department release on Verkada.
Who can make you pay, and how much
Under 15 U.S.C. 7706, the FTC, certain other federal agencies (banking regulators among them), states and internet access services can enforce the Act:
| Who sues | What they can recover per email | Cap | Can a court raise it? |
|---|---|---|---|
| FTC | Up to $53,088 per violating email | The court weighs culpability, prior conduct, ability to pay and more | No treble clause; consumer redress possible |
| State attorney general or official | Up to $250 per unlawful email to residents, or actual loss if greater | $2,000,000, except header violations | Yes, up to three times |
| Internet access service, header violations | Up to $100 per email, or actual loss if greater | No cap | Yes, up to three times |
| Internet access service, other violations | Up to $25 per email, or actual loss if greater | $1,000,000 | Yes, up to three times |
Source: 16 CFR 1.98(d), 15 U.S.C. 45(m) and 7706 (read 3 November 2026); other agencies’ amounts are not covered. At the full $250, a state hits its $2 million cap at 8,000 emails to its residents; at the full $25, an internet access service hits $1 million at 40,000.
A state needs a “pattern or practice” for opt-out, label and address failures (7704(a)(3) to (5)), but can sue over a single email with “materially false or materially misleading” header information (a)(1), or a subject line the sender knows is likely to mislead (a)(2), among others. An internet access service needs a pattern for (a)(2) to (5) and can sue over a single (a)(1) or 7704(b) violation, among others.
What the FTC has obtained
Under 15 U.S.C. 45(m), the court weighs “the degree of culpability, any history of prior such conduct, ability to pay”, among other factors, and the FTC’s guide says you “may be required to pay redress to consumers”.
In August 2024 the FTC announced a $2.95 million penalty against Verkada, “the largest penalty obtained by the FTC for a CAN-SPAM violation.” According to the complaint, as the FTC’s release describes it, Verkada sent “more than 30 million commercial emails over a three-year period”: under 10 cents per email sent. The Justice Department said the complaint alleged emails that “failed to clearly and conspicuously notify recipients of their opportunity to opt out,” no valid physical postal address, and opt-outs not honored within ten business days. In August 2023 the FTC said it would require Experian Consumer Services to pay $650,000 to settle charges that it sent consumers unsolicited email with no way to opt out.
My read: plan around the basics that case was about, not the $53,088 maximum.
What can raise damages up to three times
In a state or internet access service case, a court can raise the statutory damages up to three times for a violation committed “willfully and knowingly”, or one that included an aggravated violation under 15 U.S.C. 7704(b): sending an email that already breaks 7704(a) to addresses you knew, or should have known, were harvested by automated means from a site whose notice said it would not give, sell or transfer them, or generated by “combining names, letters, or numbers into numerous permutations,” or using scripts to register multiple accounts for such email. At three times, the caps rise to $6 million and $3 million. Ask how any list you buy was built (see whether buying email lists is legal).
When it becomes a crime
Under 18 U.S.C. 1037, some conduct is a crime: knowingly and materially falsifying header information in multiple commercial emails you intentionally send, or registering “five or more electronic mail accounts or online user accounts or two or more domain names” under a materially falsified identity and intentionally sending multiple commercial emails from them. Register sending domains truthfully (see whether cold email from a secondary domain is legal).
For those offenses, the penalty is a fine, prison or both: up to one year; up to three years if, among other triggers, more than 2,500 emails went out in 24 hours, 25,000 in 30 days or 250,000 in a year; up to five years if the offense furthered a felony or followed a prior conviction. Forfeiture can also apply.
“Nobody gets fined for cold email, so the footer can wait.”
The record FTC case alleged opt-out notices that were not clear and conspicuous, no valid postal address and opt-outs not honored within 10 business days.
Every template carries an ad label, a postal address and an opt-out notice that works.
Opt-outs honored within 10 business days, from one suppression list across every inbox.
Can a recipient sue you?
Not on my reading. Section 7706 names the FTC, other federal agencies, states and internet access services, and I read it as giving a recipient no claim of their own; I am not citing a court ruling. 15 U.S.C. 7707(b) supersedes state laws that expressly regulate commercial email “except to the extent that any such statute, regulation, or rule prohibits falsity or deception”. My reading is that this leaves room for California’s Business and Professions Code 17529.5, which covers email ads sent from California or to a California address: a recipient of an unsolicited one can recover $1,000 per email, up to $1 million per incident, for a third party’s domain used without permission, falsified, misrepresented or forged headers, or a subject line the sender knows is likely to mislead about a material fact.
Outside the US, different laws apply (see cold email laws by country, or cold email laws in Finland for one example).
Four checks before your next send
Here is what I would do this week:
Audit one live email against the basics
Header information that is accurate, a subject line that does not mislead, a clear and conspicuous note that it is an advertisement unless the recipient gave prior affirmative consent, a valid physical postal address (see the CAN-SPAM address requirement) and a clear and conspicuous opt-out notice.
Make opt-outs stick within 10 business days
The opt-out mechanism must keep working for at least 30 days after you send, and one suppression list should cover every inbox and tool you send from (see the CAN-SPAM unsubscribe rules).
Know where every address came from
No addresses harvested from sites that promise not to share them, and no permutation guessing. Knowingly using either for an email that already breaks the Act is an aggravated violation, one of the two grounds for raising damages up to three times.
Run your prevention practices, and write them down
In a state or internet access service case, the court may consider whether you established and implemented, with due care, practices designed to prevent violations. A written policy helps only if your team follows it. If an agency sends for you, both of you can be held responsible (see CAN-SPAM liability for agencies).
My team’s record: 500+ projects delivered across 30 countries. The email infrastructure we set up includes RFC 8058 one-click unsubscribe and a suppression list. Honoring opt-outs on time still depends on your own process. For mailbox costs, see our email hosting cost breakdown.
The bottom line
Treat $53,088 as the FTC’s per-email ceiling, not the bill, and remember the states and internet access services. Fix the basics, make opt-outs stick and keep your prevention practices running. I am not a lawyer. This is general information, not legal advice.